HOTSPOT
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Hot Area:
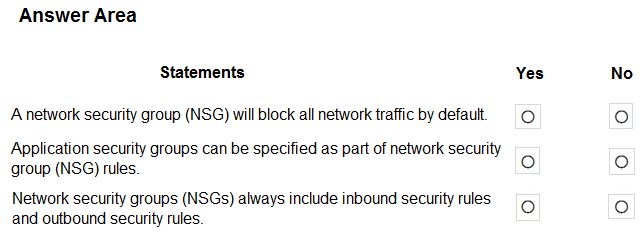
A network security group (NSG) will block all network traffic by default >> A network security group does not encrypt network traffic. It works in a similar way to a firewall in that it is used to block or allow traffic based on source/destination IP address, source/destination ports and protocol
Applications security group can be specified as part of network security group (NSG) rules >> In a NSG you can have up to 1000 NSG rules. In max 100 of this 1000 NSG rules you can specify an Application Security Group as a source or destination
Network security groups (NSGs) always include inbound security rules and outbound security rules >> A network security group contains security rules that allow or deny inbound network traffic to, or outbound network traffic from, several types of Azure resources.
Answer: No Yes Yes
2 more highly voted comments
chael88▲ 7Highly votedDecember 22, 2022 11:25 pm
Q1.NO.
By default, all inbound traffic is blocked and all outbound traffic is allowed. So the answer is NO since not all traffic is blocked.
iowaporter▲ 7Highly votedNovember 08, 2022 01:49 am
The NSG will block all Internet inbound traffic by default. But it will allow other network traffic such as AllowVNetInBound.
https://learn.microsoft.com/en-us/azure/virtual-network/network-security-groups-overview#default-security-rules
Applications security group can be specified as part of network security group (NSG) rules >> In a NSG you can have up to 1000 NSG rules. In max 100 of this 1000 NSG rules you can specify an Application Security Group as a source or destination
Network security groups (NSGs) always include inbound security rules and outbound security rules >> A network security group contains security rules that allow or deny inbound network traffic to, or outbound network traffic from, several types of Azure resources.
Answer: No Yes Yes